Digital forensics investigation is the disciplined science of identifying, collecting, preserving, analyzing, and presenting electronic evidence in a manner that guarantees legal admissibility in court. From corporate fraud and insider intellectual property theft to state-sponsored cyber espionage, digital forensic practitioners uncover the undeniable digital truth behind complex cyber incidents.
1. The Four Phases of the Digital Forensics Investigation Lifecycle
To withstand judicial challenge, examiners adhere strictly to standardized international forensics standards (ISO/IEC 27037):
- Phase 1: Identification & Scene Assessment: Identifying all potential digital artifacts relevant to the investigation—including physical workstations, mobile devices, IoT hardware, volatile RAM, server log repositories, and cloud backups.
- Phase 2: Collection & Evidence Acquisition: Safely acquiring digital evidence without altering its contents. Mobile devices are shielded in Faraday bags to block remote wiping signals, and physical media is connected through hardware write-blockers before acquisition.
- Phase 3: Scientific Examination & Analysis: Utilizing forensic software suites to reconstruct timelines, extract hidden and deleted files from unallocated space, inspect system registry artifacts, and parse event logs.
- Phase 4: Reporting & Courtroom Presentation: Preparing a clear, comprehensive, and objective forensic audit report detailing methodologies, hash verifications, findings, and expert witness conclusions.
2. Forensic Bit-Stream Imaging vs. Standard File Copying
A foundational legal rule of digital forensics is that examiners never analyze evidence on live physical media directly. Instead, they create an exact, sector-by-sector duplicate known as a Bit-Stream Forensic Image:
| Feature | Standard File Copy (Ctrl+C / Copy-Paste) | Forensic Bit-Stream Image (.E01 / .DD) |
|---|---|---|
| Scope | Only active, visible files recognized by OS | Every physical sector: MBR, slack space, unallocated clusters |
| Deleted Data | Excludes deleted file remnants | Captures deleted files and partial file fragments |
| File Timestamps | Modifies Access/Creation metadata | Preserves 100% of original MAC (Modified, Accessed, Created) times |
| Write Protection | None; host OS writes metadata to disk | Requires hardware or software write-blockers |
3. Cryptographic Hashing and the Chain of Custody
To substantiate that evidence has not been planted, modified, or tampered with, two strict procedural controls are enforced:
- Cryptographic Hash Integrity: Immediately prior to and following forensic imaging, examiners compute mathematical hashes (SHA-256 or MD5) of both the original evidentiary drive and the acquired image. An identical hash value proves mathematical identity to the legal standard of beyond a reasonable doubt.
- Chain of Custody: A rigorous chronological document tracking every transfer, inspection, analysis, and storage location of the physical and digital evidence. Any unrecorded custody gap can lead to evidence suppression in legal proceedings.
4. Volatile Memory Forensics & The Order of Volatility
Modern sophisticated malware resides strictly in volatile RAM to evade traditional disk scans. Examiners follow the Order of Volatility (RFC 3227), capturing the most ephemeral data first:
- CPU Registers, Cache, and State
- Main System Memory (RAM, active network connections, process memory)
- Temporary File Systems, Swap Space, Routing Tables
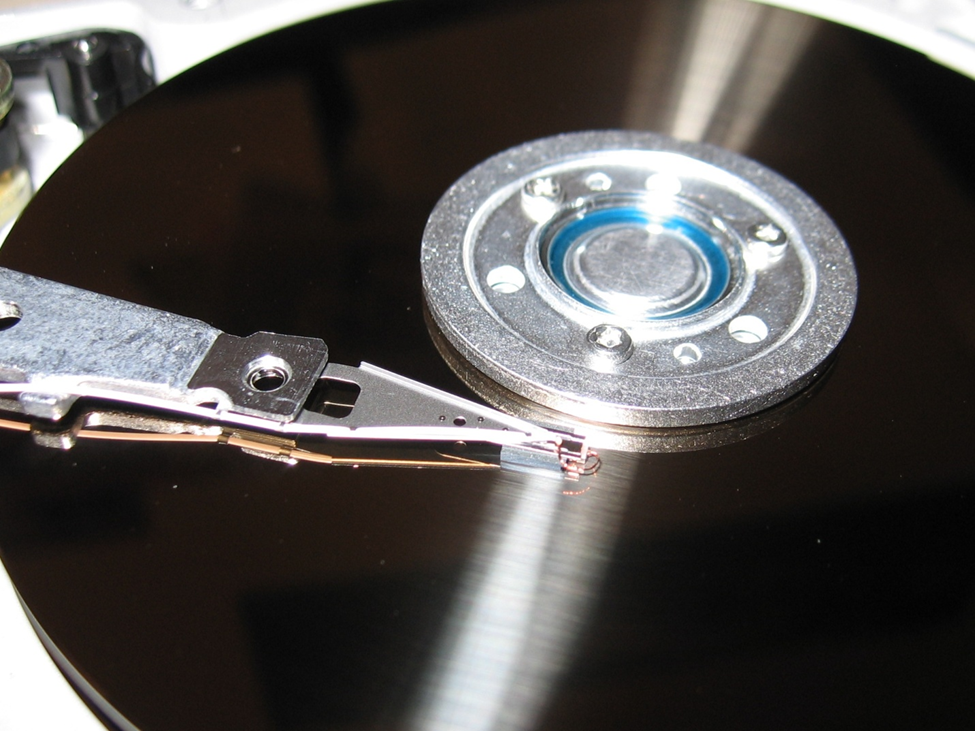
- Hard Disks and Non-Volatile Storage Media
- Remote Log Repositories and Archived Media
Frequently Asked Questions (FAQ)
Why must examiners use a hardware write-blocker?
When an operating system detects a newly plugged-in storage drive, it automatically writes hidden metadata, volume labels, and access timestamps to the disk. A write-blocker intercepts and silences all write signals, guaranteeing that not a single bit of evidence is altered.
What is file carving in digital forensics?
File carving is the process of recovering deleted files from raw unallocated disk clusters based purely on file headers and footers (magic numbers), bypassing corrupted or missing file system master tables.
What makes digital evidence legally admissible?
Evidence is admissible if it is relevant, authentic, acquired through scientifically accepted methodologies (Daubert/Frye standards), verifiable via cryptographic hashes, and supported by a continuous, unbroken chain of custody.
Conclusion
A rigorous digital forensics investigation demands absolute technical precision, scientific discipline, and adherence to legal principles. By preserving evidence with cryptographic hashing, respecting the order of volatility, and maintaining an unbroken chain of custody, investigators uncover the decisive digital evidence required to uphold justice.
Anti-Forensics Countermeasures & Super-Timeline Reconstruction
Sophisticated attackers frequently attempt anti-forensics measures, including timestamp forgery (timestomping), log wiping, and volume shadow copy deletion. Forensic analysts counter these evasions by compiling unified super-timelines from multiple independent artifact sources.
- MFT Record Attribute Verification: Compare standard file information ($SI) timestamps against file name ($FN) attributes inside the NTFS Master File Table to expose forged modification dates.
- Shimcache & Amcache Forensics: Extract execution history and binary file paths even after malicious executables have been deleted from disk storage.
- USN Journal Analysis: Parse the Update Sequence Number (USN) journal to reconstruct file creation, modification, and truncation activity independent of Windows Event Logs.